As breach costs reach new highs on both sides of the border, the Cybersecurity & Identity Summit returns to Ottawa on May 3–4, 2027, with complimentary registration open through the end of this year
October is Cybersecurity Awareness Month, and this year the subject feels less like an awareness campaign and more like a line item.
The 2026 Cost of a Data Breach Report, released in late July and based on more than 600 breached organizations, put the global average cost of a breach at a record $4.99 million. In the United States, the average climbed to $11.5 million, up 11 percent from the prior year. In Canada, organizations paid a record CA$7.11 million per breach on average, the highest level since the study began.
Figures like these have moved cybersecurity out of the server room and onto the agenda of CEOs, CFOs, and boards. They also explain why a growing number of business leaders are looking for places where policymakers, security practitioners, and executives can work through these issues together.
One of those places is the Cybersecurity & Identity Summit (CIS) 2027, which will be held May 3–4, 2027, at the Rogers Centre Ottawa.
A Steady Stream of Reminders
Recent weeks have shown how broad the exposure has become.
In late September, Arizona’s state court system disclosed a cyberattack that, according to an update reported on October 7, gave criminals access to names, Social Security numbers, and case details for more than 1.3 million people, along with sensitive foster care records. Investigators believe it began with a single phishing email clicked by an employee.
In Chicago, a ransomware attack temporarily disrupted systems at a major public university’s medical school, with attackers stealing data from its servers. And in Toronto, a leading children’s hospital disclosed in August that a flaw in third-party software had exposed personal information belonging to current and former employees and job applicants.
The broader numbers point the same way. One ransomware-tracking firm counted 789 organizations listed on ransomware leak sites in September 2026. U.S. organizations made up 41 percent of those claimed victims, and Canada ranked second for the first time this year. Healthcare was the most targeted sector for the fourth consecutive month.
The Common Thread: Identity
Many of these incidents share a quiet starting point. Attackers increasingly do not need to break in when they can simply log in.
The 2026 Data Breach Investigations Report, which examined more than 22,000 confirmed breaches, found credential abuse in 39 percent of full breach chains. Phishing, stolen passwords, and hijacked sessions allow intruders to move through systems looking like ordinary users.
Artificial intelligence is adding speed and polish to these tactics. More than one in four organizations hit by a malicious attack over the past year said AI drove it, and deepfake impersonation accounted for close to half of those AI-driven attacks. At the same time, employees using unapproved AI tools, often called “shadow AI,” figured in 43 percent of security incidents, more than double the previous year.
Response times are also slipping. The average time to identify and contain a breach rose to 247 days, ending five straight years of improvement. Supply chain compromise, where a trusted partner becomes the entry point, now adds more to the cost of a breach than any other single factor, both globally and in Canada.
For business leaders, the implication is that cybersecurity decisions are increasingly decisions about people, partners, and governance, areas that sit squarely within the executive suite.
About the Summit
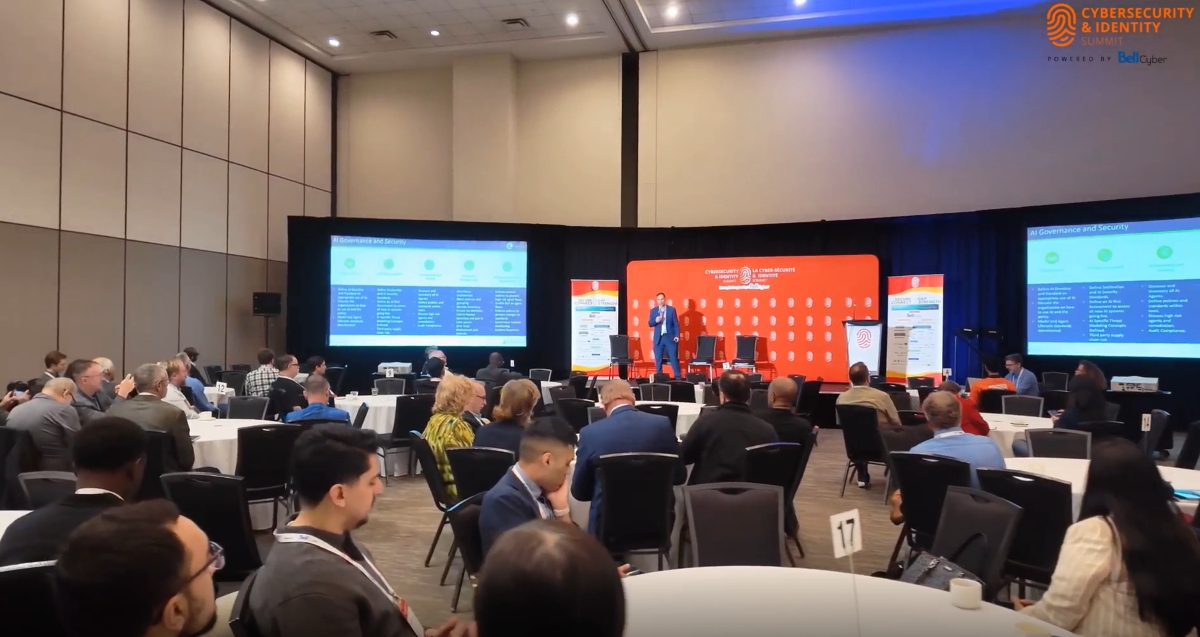
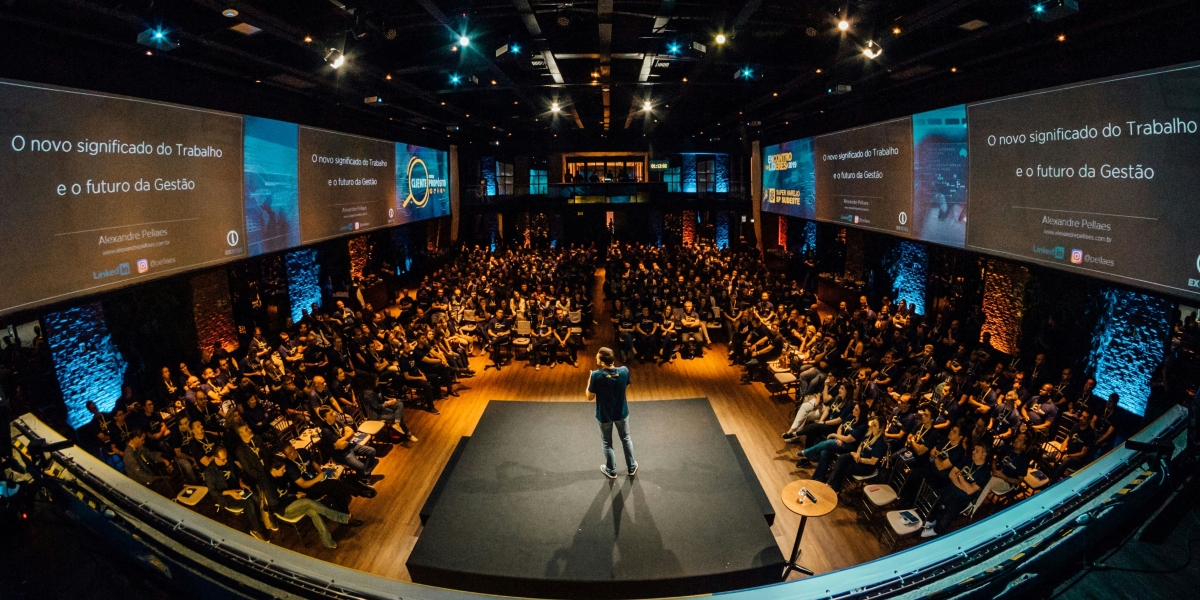
Now approaching its eighth edition, CIS has grown into one of North America’s established forums for cybersecurity and digital identity. It brings together government leaders, industry executives, security professionals, and researchers from across Canada, the United States, and internationally.
The 2026 edition, held under the theme “Beyond Trust: Secure the AI Era,” organized its program around four areas that closely track the trends above:
- Leadership, Policy & Cyber Governance
- AI and Quantum
- Securing the Supply Chain
- The Human Factor, Education & Emerging Frontiers
The summit’s contribution to the region was recognized when CIS 2025 received the Think Ottawa Leader Award for bringing global innovation and industry leadership to Canada’s capital.
Why It Is Relevant Beyond Ottawa
For U.S. executives, a gathering in Canada’s capital may not be the obvious choice, but the cross-border dimension is part of its value.
Canadian and American organizations share suppliers, cloud infrastructure, customers, and increasingly the same attackers. Given that supply chain compromise is now the leading driver of breach costs, risk rarely stops at a national boundary. CIS places policymakers and private-sector leaders from both countries in the same setting, offering an early view of the frameworks and expectations likely to shape cross-border business.
The program is also built with decision-makers in mind. In addition to technical sessions, past editions have included C-suite master classes and leadership forums, along with dedicated networking time for meeting peers, speakers, and public-sector counterparts. For executives weighing where to invest, how to govern AI use, and how to prepare their organizations for an incident, that format allows for practical, candid discussion.
What to Expect at CIS 2027
Based on the summit’s established format, the two-day program at the Rogers Centre Ottawa is expected to include:
- Keynotes and panel discussions with government, industry, and academic leaders
- Executive master classes on cyber governance, AI risk, and resilience
- Workshops for security and IT teams
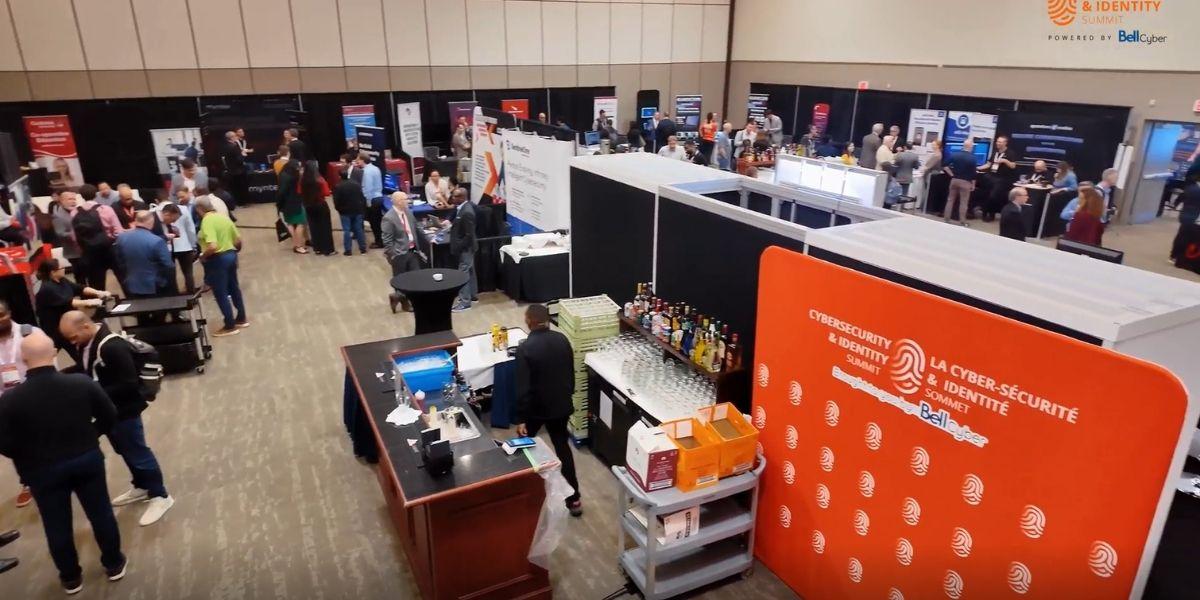
- An exhibition area featuring identity, AI security, and threat-defense solutions
- Structured networking for executives and public-sector partners
The 2027 theme, speaker lineup, and full agenda will be published at cis-events.com.
Complimentary Registration Through December 31
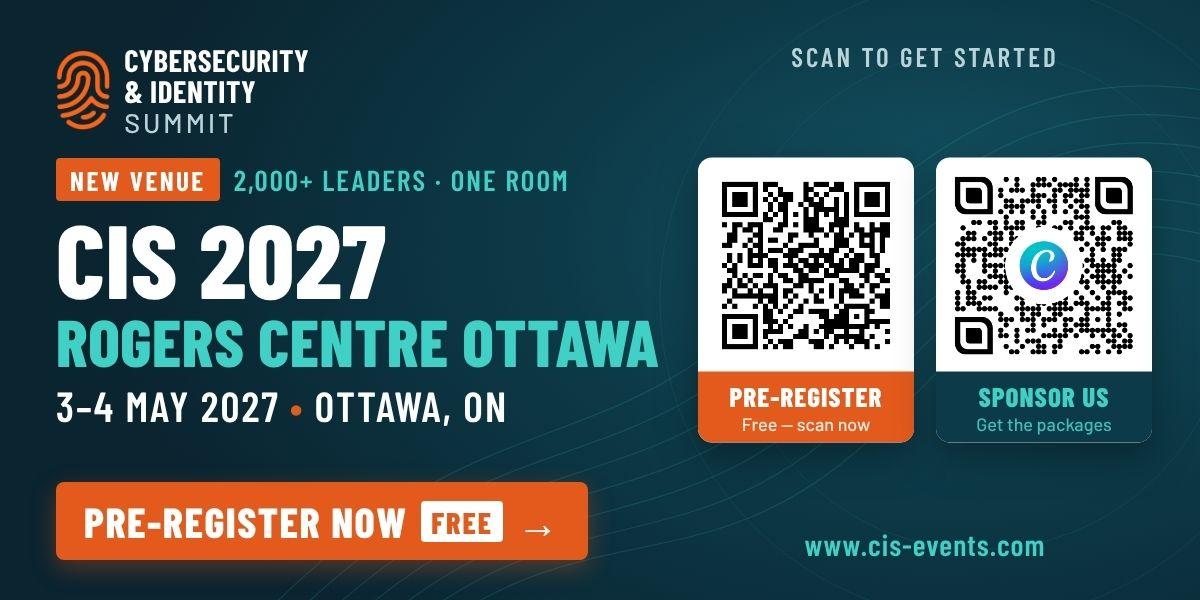
Organizers are offering free admission to CIS 2027 for those who register before December 31, 2026. For leaders finalizing next year’s plans, it is an opportunity to reserve a place early and consider which members of their security, risk, legal, and executive teams should attend.
Registration is available at [registration link]. Organizations interested in speaking or partnership opportunities can reach the CIS team at info@cisummit.ca.
Looking Ahead
Record breach costs, AI-assisted impersonation, and a steady flow of incidents across healthcare, education, government, and industry have made cybersecurity and digital identity a shared leadership responsibility.
CIS 2027 offers North American business leaders a cross-border setting to understand those risks and compare approaches with peers, and for the rest of this year, a seat comes at no cost.